AI-NATIVE SAST

Find the vulnerabilities your last scanner missed.

Put frontier models across your whole codebase and find the exploitable vulnerabilities before Mythos-level attackers do.

THE OUTCOME
Identify exploitable issues, with context
Get Started
payments-api - main
Full codebase review
src/
api/
billing.ts–
export.ts!
webhooks.ts!
auth/
session.ts–
roles.ts!
lib/
db.ts
scripts/
seed.ts–
Exploitable findings
Last scanner1
Dam Secure3
Missing auth check
api/export.ts
Missed before
Privilege escalation
auth/roles.ts
Missed before
SSRF in webhook handler
api/webhooks.ts
Not exploitable
Hard-coded tokenscripts/seed.ts
Test seed data, never deployed.
SQL injectionauth/session.ts
ID is cast to an integer upstream.
Open redirectapi/billing.ts
Only redirects to allowlisted paths.

Trusted by modern engineering teams
Skip logo
Dovetail logo
Serval logo
Pluss communities logo
Doug Rathbone, VP of Engineering at Dovetail
"Shortly after set-up, Dam Secure found a critical finding in a long-standing feature. It paid for itself very quickly."
Doug Rathbone
VP of Engineering
THE PROBLEM WITH OTHER SCANNERS

Scanners flag everything...
‍
except what matters.

01

Noisy results hide the real issues.

Pattern matching flags anything that looks risky, without checking if it’s reachable or as severe as it looks. Teams triage the first page of results and stop, and the real vulns sit in the backlog.

02

Every security scan starts from zero.

Reviews that don't remember past results re-flag issues your team already dismissed. Your team ends up re-triaging the same findings every quarter.

03

Business logic flaws slip through.

Without understanding how your codebase fits together, a review can’t tell when an access check is missing or a workflow can be abused. AI-generated code carries 172% more of these flaws.
OUR SOLUTION

Only surface what’s
‍actually exploitable.

Get Started
Less Noise

Every finding triaged before it hits your backlog.

AI triage checks who can reach each finding, what it would let them do and what already stands in the way, then recommends a severity with the reason behind it.

Your team works on what’s exploitable, with full context and reasoning behind the call.

payments-api - full review
SQL injection in order search
Other scanner
Critical
Dam Secure
Medium
ReachabilityAdmins only
The search route sits behind the admin panel, so only a signed-in admin can trigger it.
Attack pathreq.query.q → db.raw()
Search input flows from routes/orders.ts:18 through searchOrders() into a raw query.
ImpactOrders data
An admin could read order rows they can already see in the panel.
LikelihoodLowAssumption
Needs a compromised admin account. Assumes admin sign-in is behind SSO.
MitigationsAudit logged
Every admin query is written to the audit log.
Recommended: MediumDeciding factor: only admins can reach it
KNOWLEDGE GRAPH

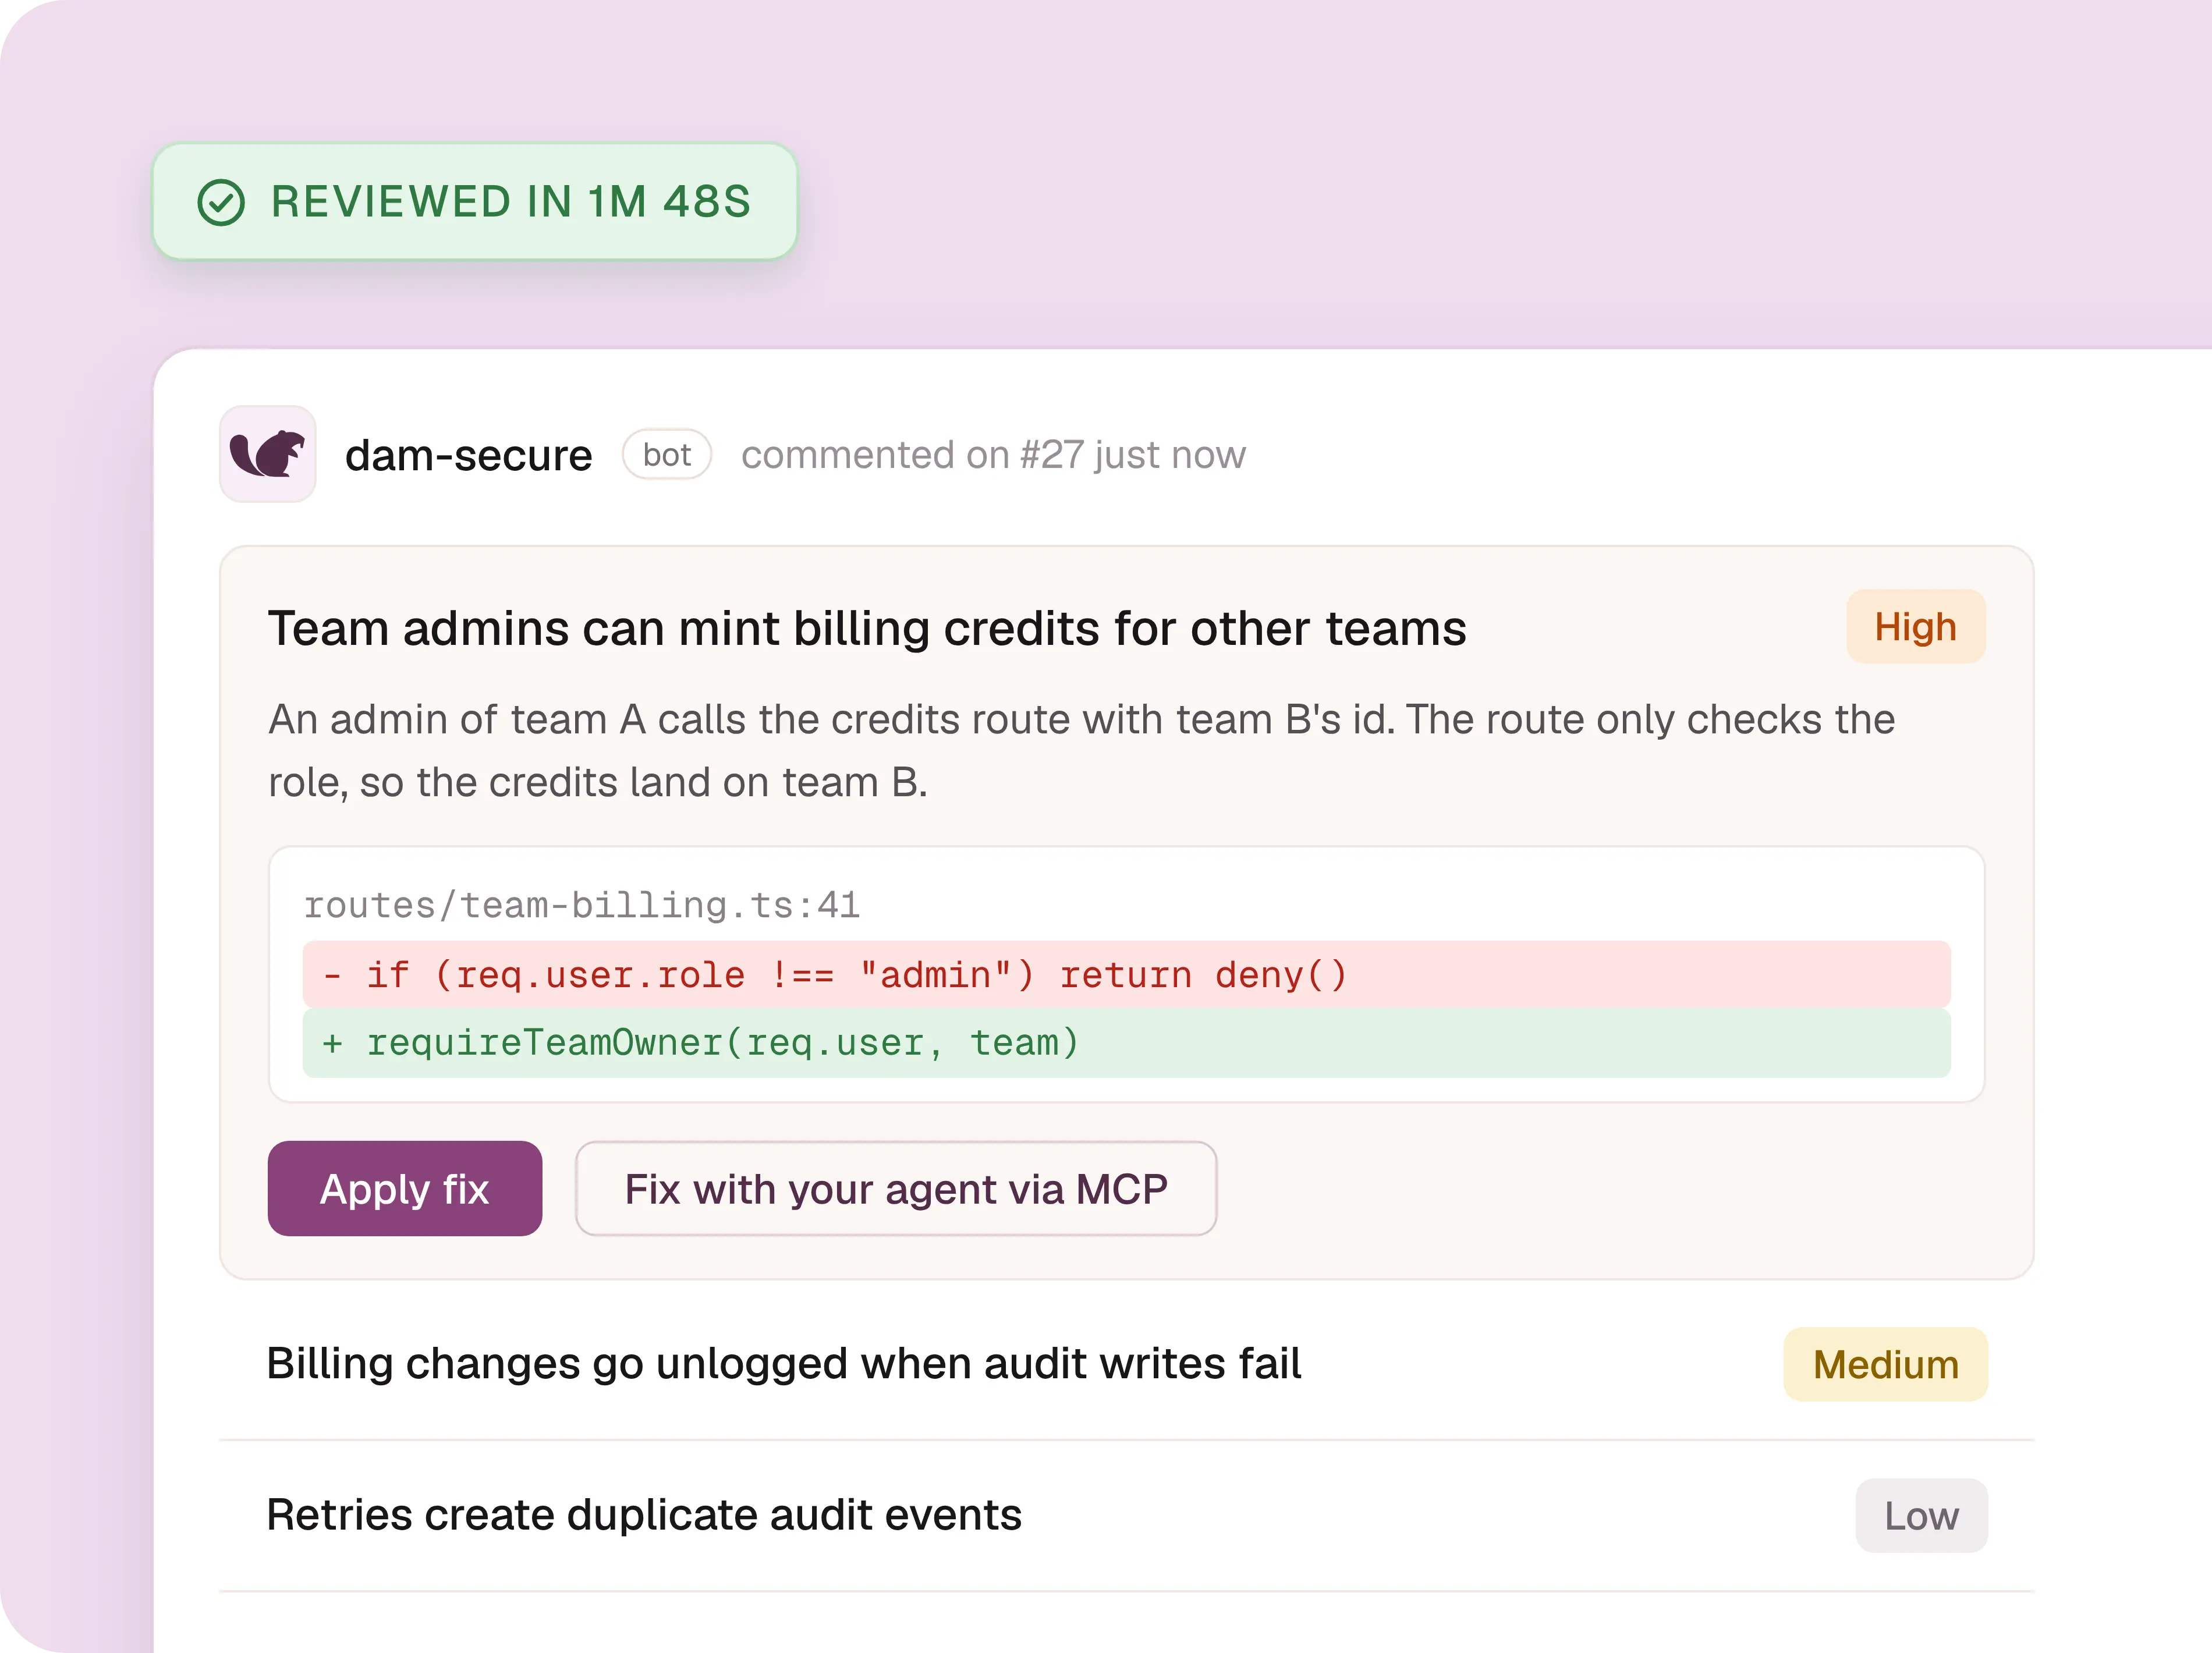
Catch business logic flaws pattern matching misses.

Dam Secure maps how your codebase fits together before it reviews a line of code. Missing access checks and abusable workflows get caught from the very first review.

routes/teams.tsDELETE /teams/:id/members/:userId
24requireAuth(req)
25await removeMember(req.params.id, req.params.userId)
Pattern matching
0 issues
Auth is called, so nothing matches a known bad pattern.
With codebase contextHigh
Missing team admin check
Every other team route checks the caller is an admin. Here, any member can remove the owner.
Apply fix
LEARNING LOOPS

Never re-triage the same finding twice.

Fixes and dismissals carry across every rescan, along with the reasons your team gave. Findings your team has already dealt with stay dealt with, and each review gets sharper than the last.

payments-api - rescan
October review
Rescan0 re-triaged
SSRF in webhook handler
Dismissed in Sep: "URLs allowlisted in config"
Stays dismissed
Hard-coded API token
Fixed in Sep by MP
Stays fixed
Missing auth check on /exportNew
AppSEC VISIBILITY

Code, secrets and dependencies in one audit-ready backlog.

Every review covers the OWASP Top 10, plus exposed secrets and vulnerable dependencies, all in one place. Every fix and dismissal is recorded with who made it and why, so you’re ready for SOC 2 audits and customer security reviews.

Backlog
All 22Code 12Secrets 3Dependencies 7
A01 AccessMissing access check on refundsOpen
SecretStripe key in config.tsFixed by JL
Dependencylodash 4.17.15 - prototype pollutionOpen
A03 InjectCommand injection in export jobDismissed by MP
"Input is a fixed enum, never user-supplied."
AI-Native Remediation

Triage and fix findings straight from your agent.

Query findings for any PR or repo over MCP, then confirm, dismiss or mark them fixed without leaving your dev environment. Ask your agent to get every issue on your PR and fix it, and the backlog updates as it goes.

Coding agentpayments-api
>Get all the Dam Secure issues on my PR and fix them
dam-secure.list_findings(pr: 412)
HighMissing auth check on /exportOpen
MediumSQL injection in order searchOpen
LowHard-coded token in seed.tsOpen
dam-secure.mark_fixed(2 findings)
dam-secure.dismiss("Test seed data, never deployed")
Fixed 2 issues and dismissed 1. Your Dam Secure backlog is up to date.
Battle-Tested Evals

The best model for every use case.

We benchmark models on real security findings to learn which types of vuln each one finds best, then route every review to the right model for the job. Dam Secure catches far more exploitable vulnerabilities than any one model would find on its own.

Recall by vuln type
OpusDeepSeekGLM
Access control94%81%76%
Injection84%91%79%
SSRF72%80%89%
Crypto misuse78%88%74%
Lower Cost

Deep codebase reviews, without the token bill.

Running a frontier model over your whole codebase gets expensive fast. Dam Secure routes each part of the review to the model that handles it best, so you get a full, deep review at a fraction of the token spend of doing it yourself.
payments-api - full review
Token spend
Same depth
Single frontier model$$$$
Dam Secure routing$
Auth flows- OpusQuery layer- DeepSeekConfig- GLM
"Dam Secure has eliminated less effective static analysis tools. We now have a much more sophisticated overview of what we’re building."
Sam Stewart, Head of Security at Serval
Thor Kappel Davis
Chief Technology Officer
AI-NATIVE SAST
3x
Less noise
Dam Secure triages every finding for reachability and existing mitigations, so your team only sees the issues that can actually be exploited.

How it works

01

Connect your repos.

Install the GitHub App, or connect GitLab, Bitbucket or Azure DevOps, and Dam Secure maps how your codebase fits together before it reviews a single line of code.

02

Get a baseline review.

Dam Secure reviews your whole default branch and triages every finding for reachability and existing mitigations, so you start with a ranked list of what’s actually exploitable.

03
MCP

Every change stays covered.

Run a new scan whenever you need one. Fix, confirm or dismiss findings from your agent over MCP, and every decision carries into the next scan, so nobody re-triages the same finding.

Works with the tools you already use

Claude logo
Cursor logo
Azure DevOps logo
Bitbucket logo
GitLab logo
GitHub Copilot logo
Slack logo
Linear logo
GET STARTED WITH DAM SECURE

Your Security.
Enforced at AI Speed.

Attackers are already using Mythos-level models to find vulnerabilities. Join the teams putting frontier models on your side first.
Abstract landscape graphic