Unrivaled PR reviews,
at a fraction of the cost.
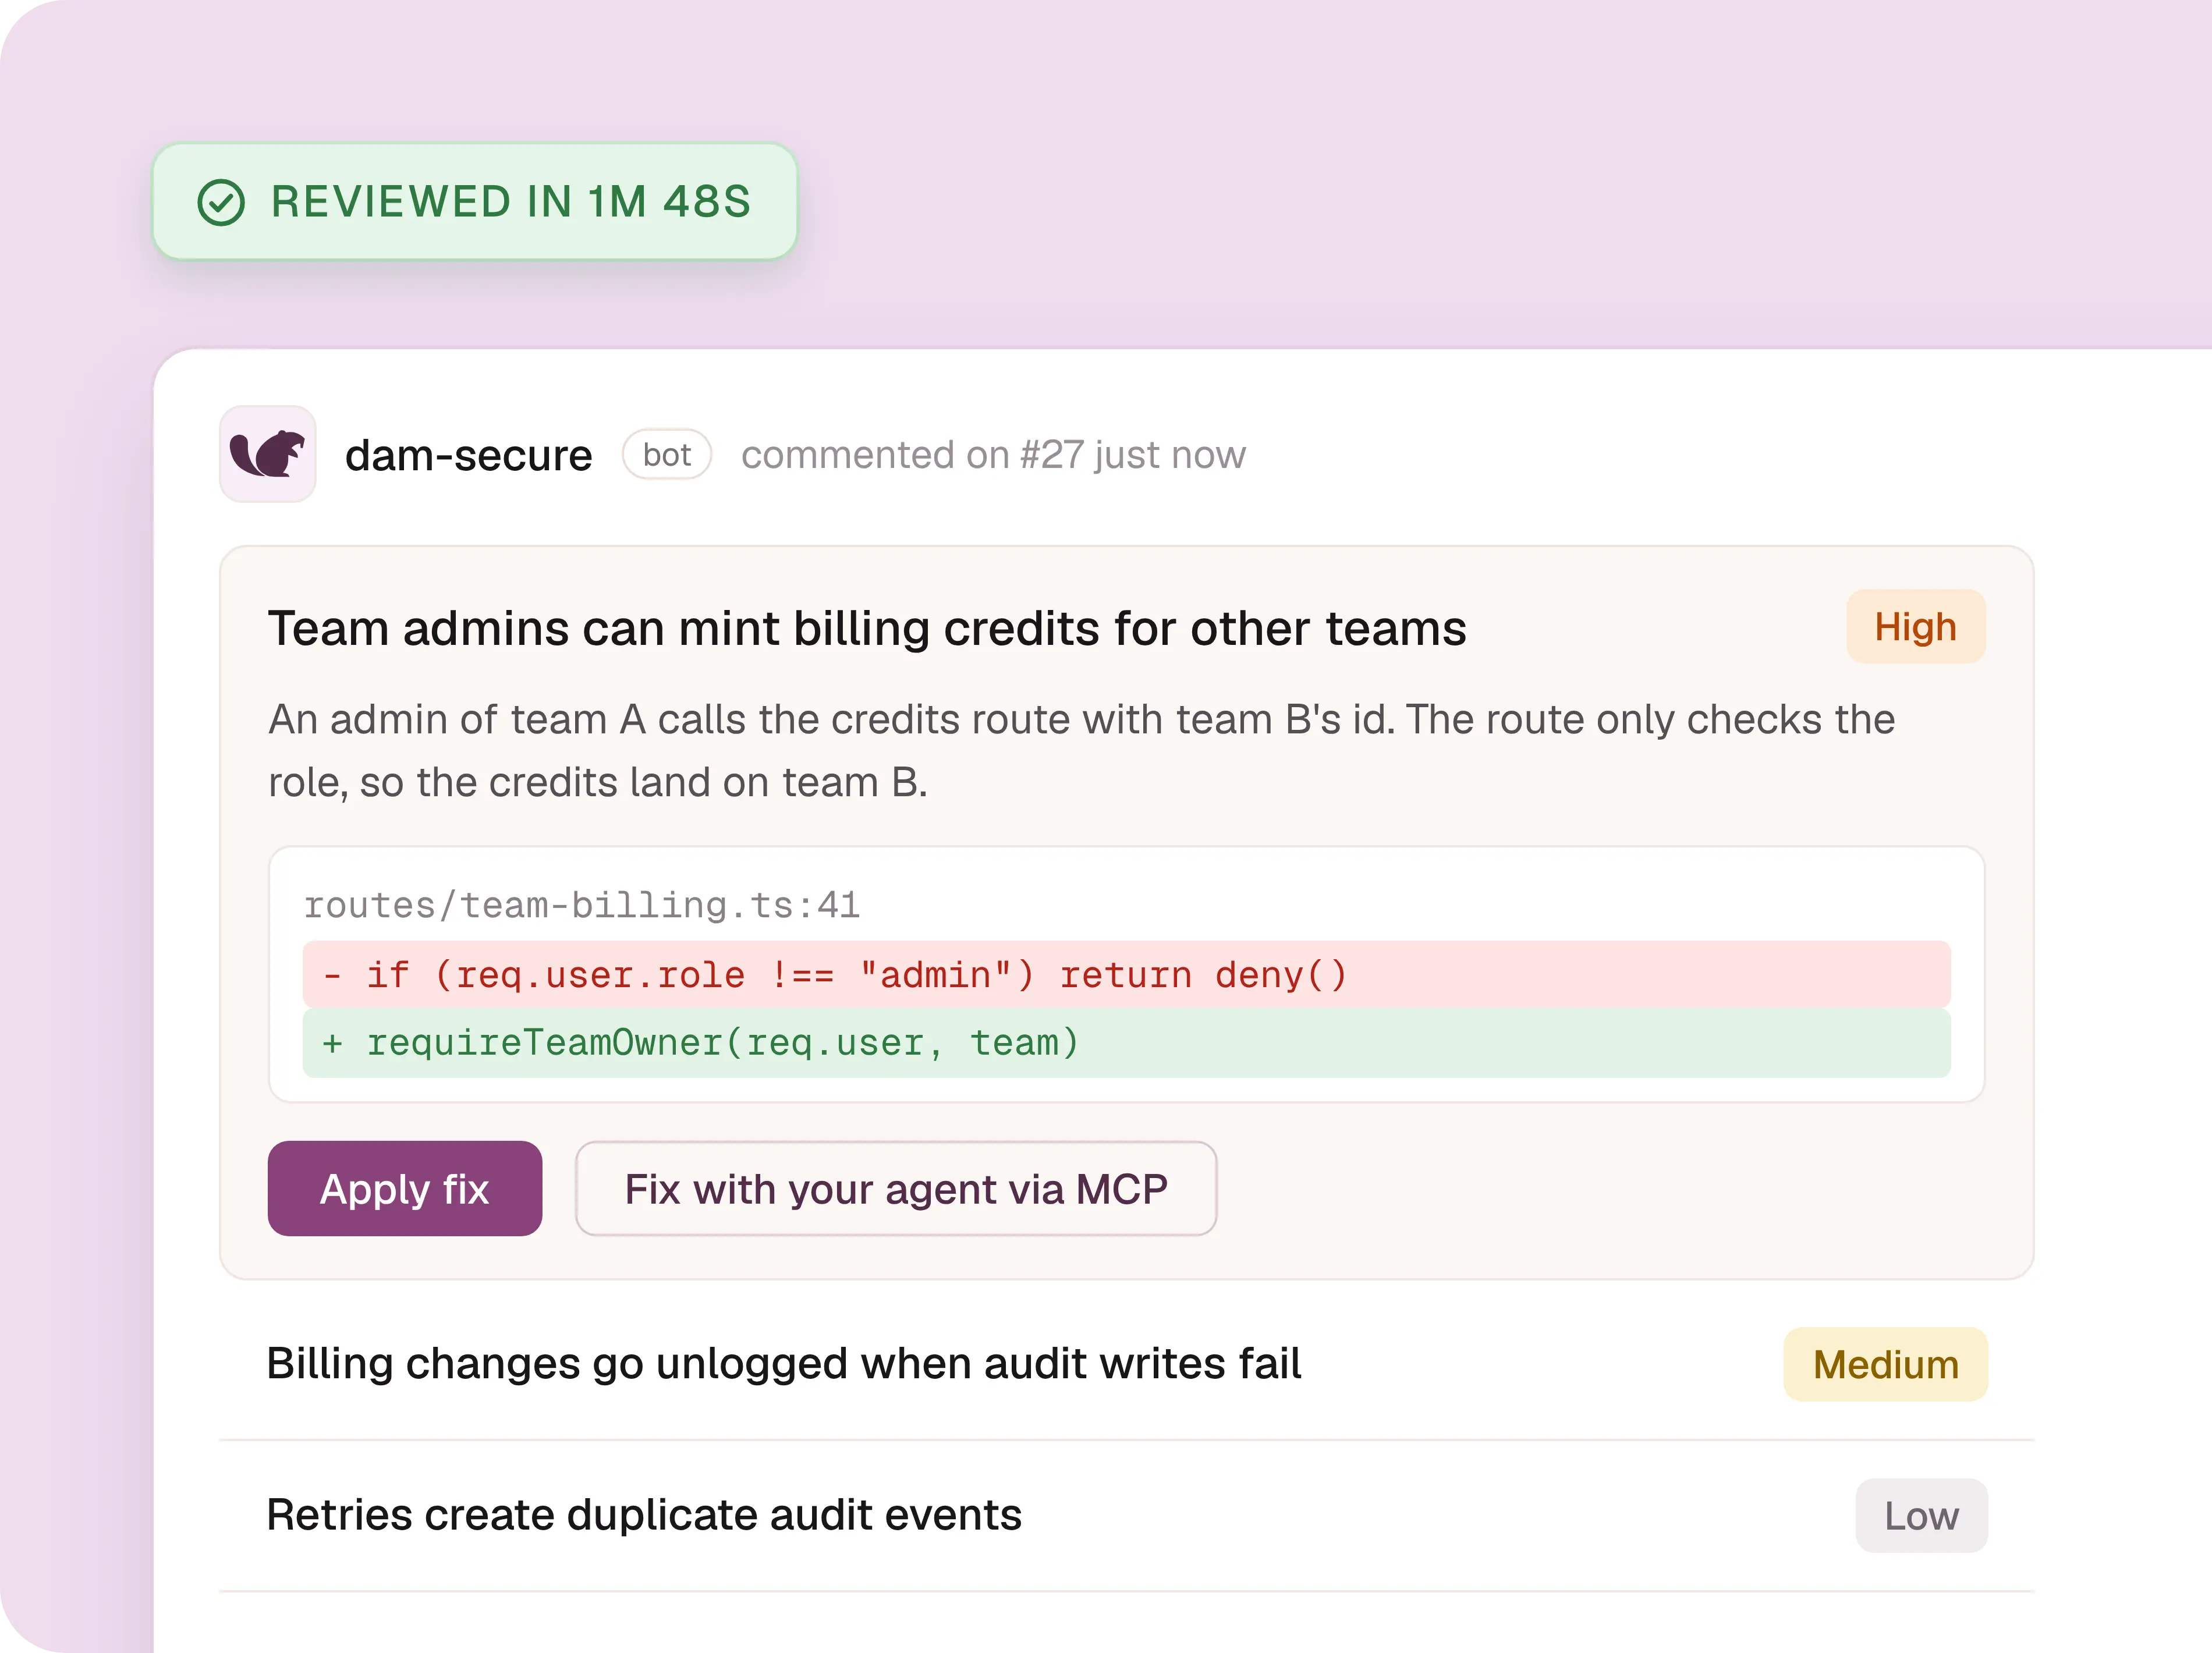
Review every pull request against how your codebase actually works, in <2 minutes. Get frontier-model findings without paying frontier-model token prices.
Trusted by modern engineering teams
“Why not just DIY?”

with Claude Code Security, Codex or DIY

with Dam Secure
AI-enabled coding has broken the old security model.
Legacy scanners don’t understand your code.
Rule-based scanners match known patterns against a fixed ruleset. They can't reason about what your code is actually trying to do, so the logic flaws and context-dependent issues that matter most slip straight through.
Agents open more PRs than any team can review.
Teams are running software factories, with agents opening pull requests around the clock. Review queues grow faster than anyone can clear them, so security review gets rationed to the PRs that look risky. Attackers using Mythos-level models don’t ration anything.
DIY’ing security review costs time & money.
Building in-house means months of engineering time spent on a security tool instead of product. And once it’s built, someone has to keep it current as threats evolve, or gaps open up that nobody notices until something ships.
The best model for every use case.
We benchmark models on real security findings and route each review to the one that performs best for that language, use case and vulnerability type.
You get more accurate findings than any single model gives you out of the box, for a fraction of the token spend.
3x fewer false positives on every PR.
AI triage checks every finding for reachability and existing mitigations, and confirms the ones that are exploitable in your code. False positives are dismissed automatically when confidence is high, so your team only sees what matters.
Findings that get sharper with every review.
Every fix, dismissal and PR comment feeds into future reviews, along with your threat models and where your code runs. A flagged false positive doesn’t come back, and known risks get checked on every change.
Findings with the fix, in under two minutes.
Security feedback arrives in under two minutes, while the change is still fresh. Developers can fix it on the PR or hand it to their coding agent, without waiting on AppSec.
Every finding, across every repo, in one backlog.
Findings are tracked as issues that sync to Linear and Slack and close automatically when the fix lands, even across stacked PRs. You know what’s still open, with a record of who fixed or dismissed and why.
Catch the business logic flaws generic reviews miss.
Dam Secure maps how your codebase fits together at onboarding and reviews every change in that context. Missing access checks and abusable workflows get caught from the very first review.
How it works
Connect your repos.
Install the GitHub App, or connect GitLab, Bitbucket or Azure DevOps. Setup is a turnkey install, so reviews start on your next PR.
Routed to the best model.
Each pull request is routed to the model that performs best for its language, use case and vulnerability type, and reviewed against how your codebase actually works.
Findings land in <2 min.
Each finding explains how to fix it, syncs to Linear and Slack, and closes automatically once the fix merges.
Works with the tools you already use



Your Security.
Enforced at AI Speed.
Attackers are already using Mythos-level models to find vulnerabilities. Join the teams putting frontier models on your side first.