Give your agents the security context they need.
Turn every vulnerability you’ve already fixed into context your coding agents follow, so the same flaws are never written twice.


Trusted by modern engineering teams
Your agents don't actually know
your security standards.
Keeping security context current is a full-time job.
Skills, rules files, AGENTS.md, linting rules: the way you guide agents keeps changing. Someone has to write that guidance for every repo and every agent, then keep it current as both evolve.
AppSec can’t be in every decision.
Agents make hundreds of design and implementation calls a day, and your AppSec team can’t review them all. Their knowledge stays with a few people while the same flaws get written across every repo.
Security turns into the blocker.
When agents don’t know your standards, issues surface late in review and changes bounce back for rework. Engineers feel slowed down, AppSec feels ignored, and the same vulnerabilities keep coming back.
All your security context, managed from one place.
Manage the security guidance your agents follow across every repo, whatever format it’s in. Always know exactly what your agents are working from.
Security context tailored to your codebase.
We map how your codebase fits together and write security context for the auth patterns, data flows and frameworks you actually use. Agents follow guidance that matches how your code really works.
Fix a flaw once and your agents stop repeating it.
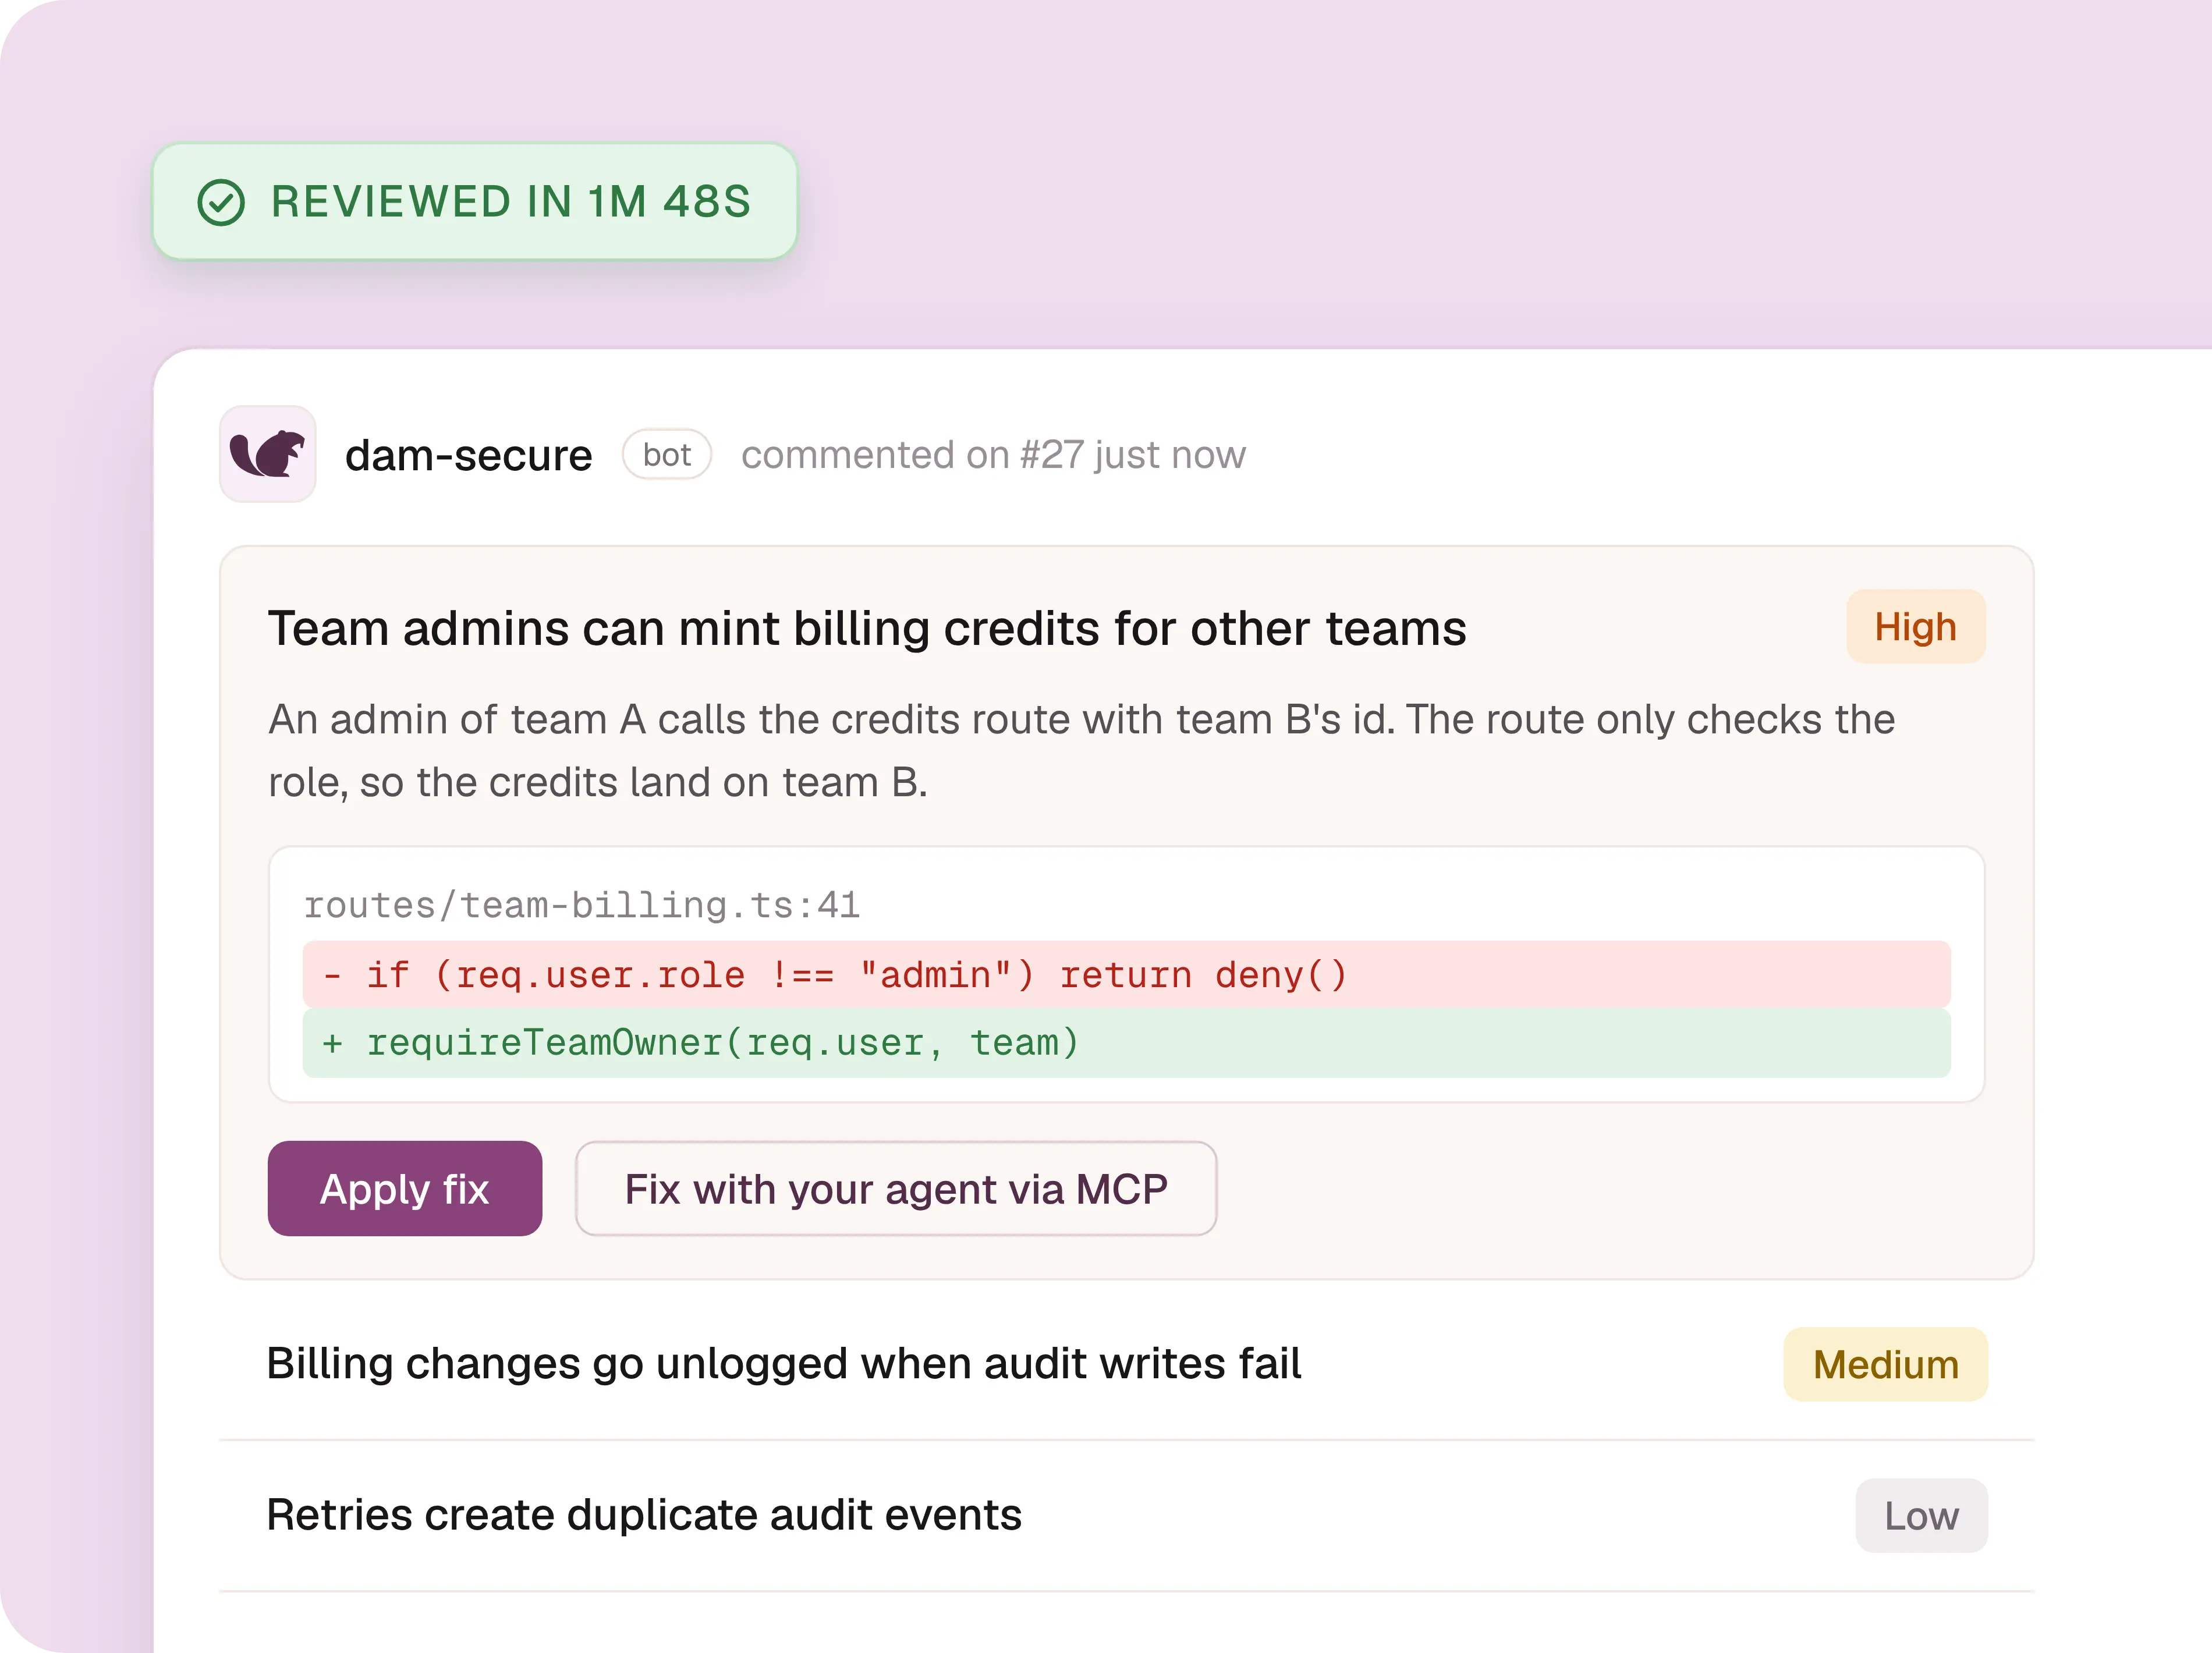
When a PR or repo review finds a vulnerability, Dam Secure turns it into guidance that stops agents writing that pattern again. Your team’s fixes and dismissals tune it too, so noisy guidance gets refined and useful guidance gets reinforced.
Security context that keeps pace with your code.
When a new service, framework or auth pattern lands, the guidance that covers it updates too. Agents stop working from guidance written for last quarter’s code.
Every coding agent covered, with nothing to install.
Context lives in the repo in the formats Claude Code, Cursor, Codex and GitHub Copilot already read, and agents load only the guidance for the code they’re touching. Devs keep working the way they do now, whichever agent they use.
Ship faster without security slowing you down.
When your security standards are built into how agents write code, changes pass review the first time. Teams ship faster, and AppSec stops being the step everyone waits on.
How it works
Connect your repos.
Dam Secure maps how your codebase works, from your auth patterns to how you handle data, so the context fits the code your agents write.
Context is tailored to your code.
Security context is generated for your codebase in the formats Claude Code, Cursor, Codex and GitHub Copilot read, then raised as a PR for your team to review.
Context evolves with your code.
As your code changes and your team fixes or dismisses findings, Dam Secure keeps security context up to date, so your agents always work from the latest guidance.
Works with the tools you already use



Your Security.
Enforced at AI Speed.
Attackers are already using Mythos-level models to find vulnerabilities. Join the teams putting frontier models on your side first.