New CVEs drop every day.
Know what affects you.
Check every open source package across your repos for known vulnerabilities, so you’re never the last to find out.
Trusted by modern engineering teams
Your code is only as safe
as its packages.
Agents install packages nobody reviewed.
Coding agents pull in new packages to get the job done, each with its own dependencies and vulnerabilities. Nobody chose them on purpose, so nobody is tracking whether they’re safe.
Nobody can see every package you depend on.
Packages are spread across every repo, language and package manager you use. When a new advisory drops, nobody can say straight away which repos are affected.
'Safe' packages don’t necessarily stay safe.
New vulnerabilities can get disclosed in packages you installed months, even years ago. Your code didn’t change, but your exposure did.
Every package, across every repo, in one view.
See every third-party package your org installs and exactly where, with anything that needs attention flagged. When anyone asks whether you’re covered, you have a confident answer.
Fix one package, clear every advisory.
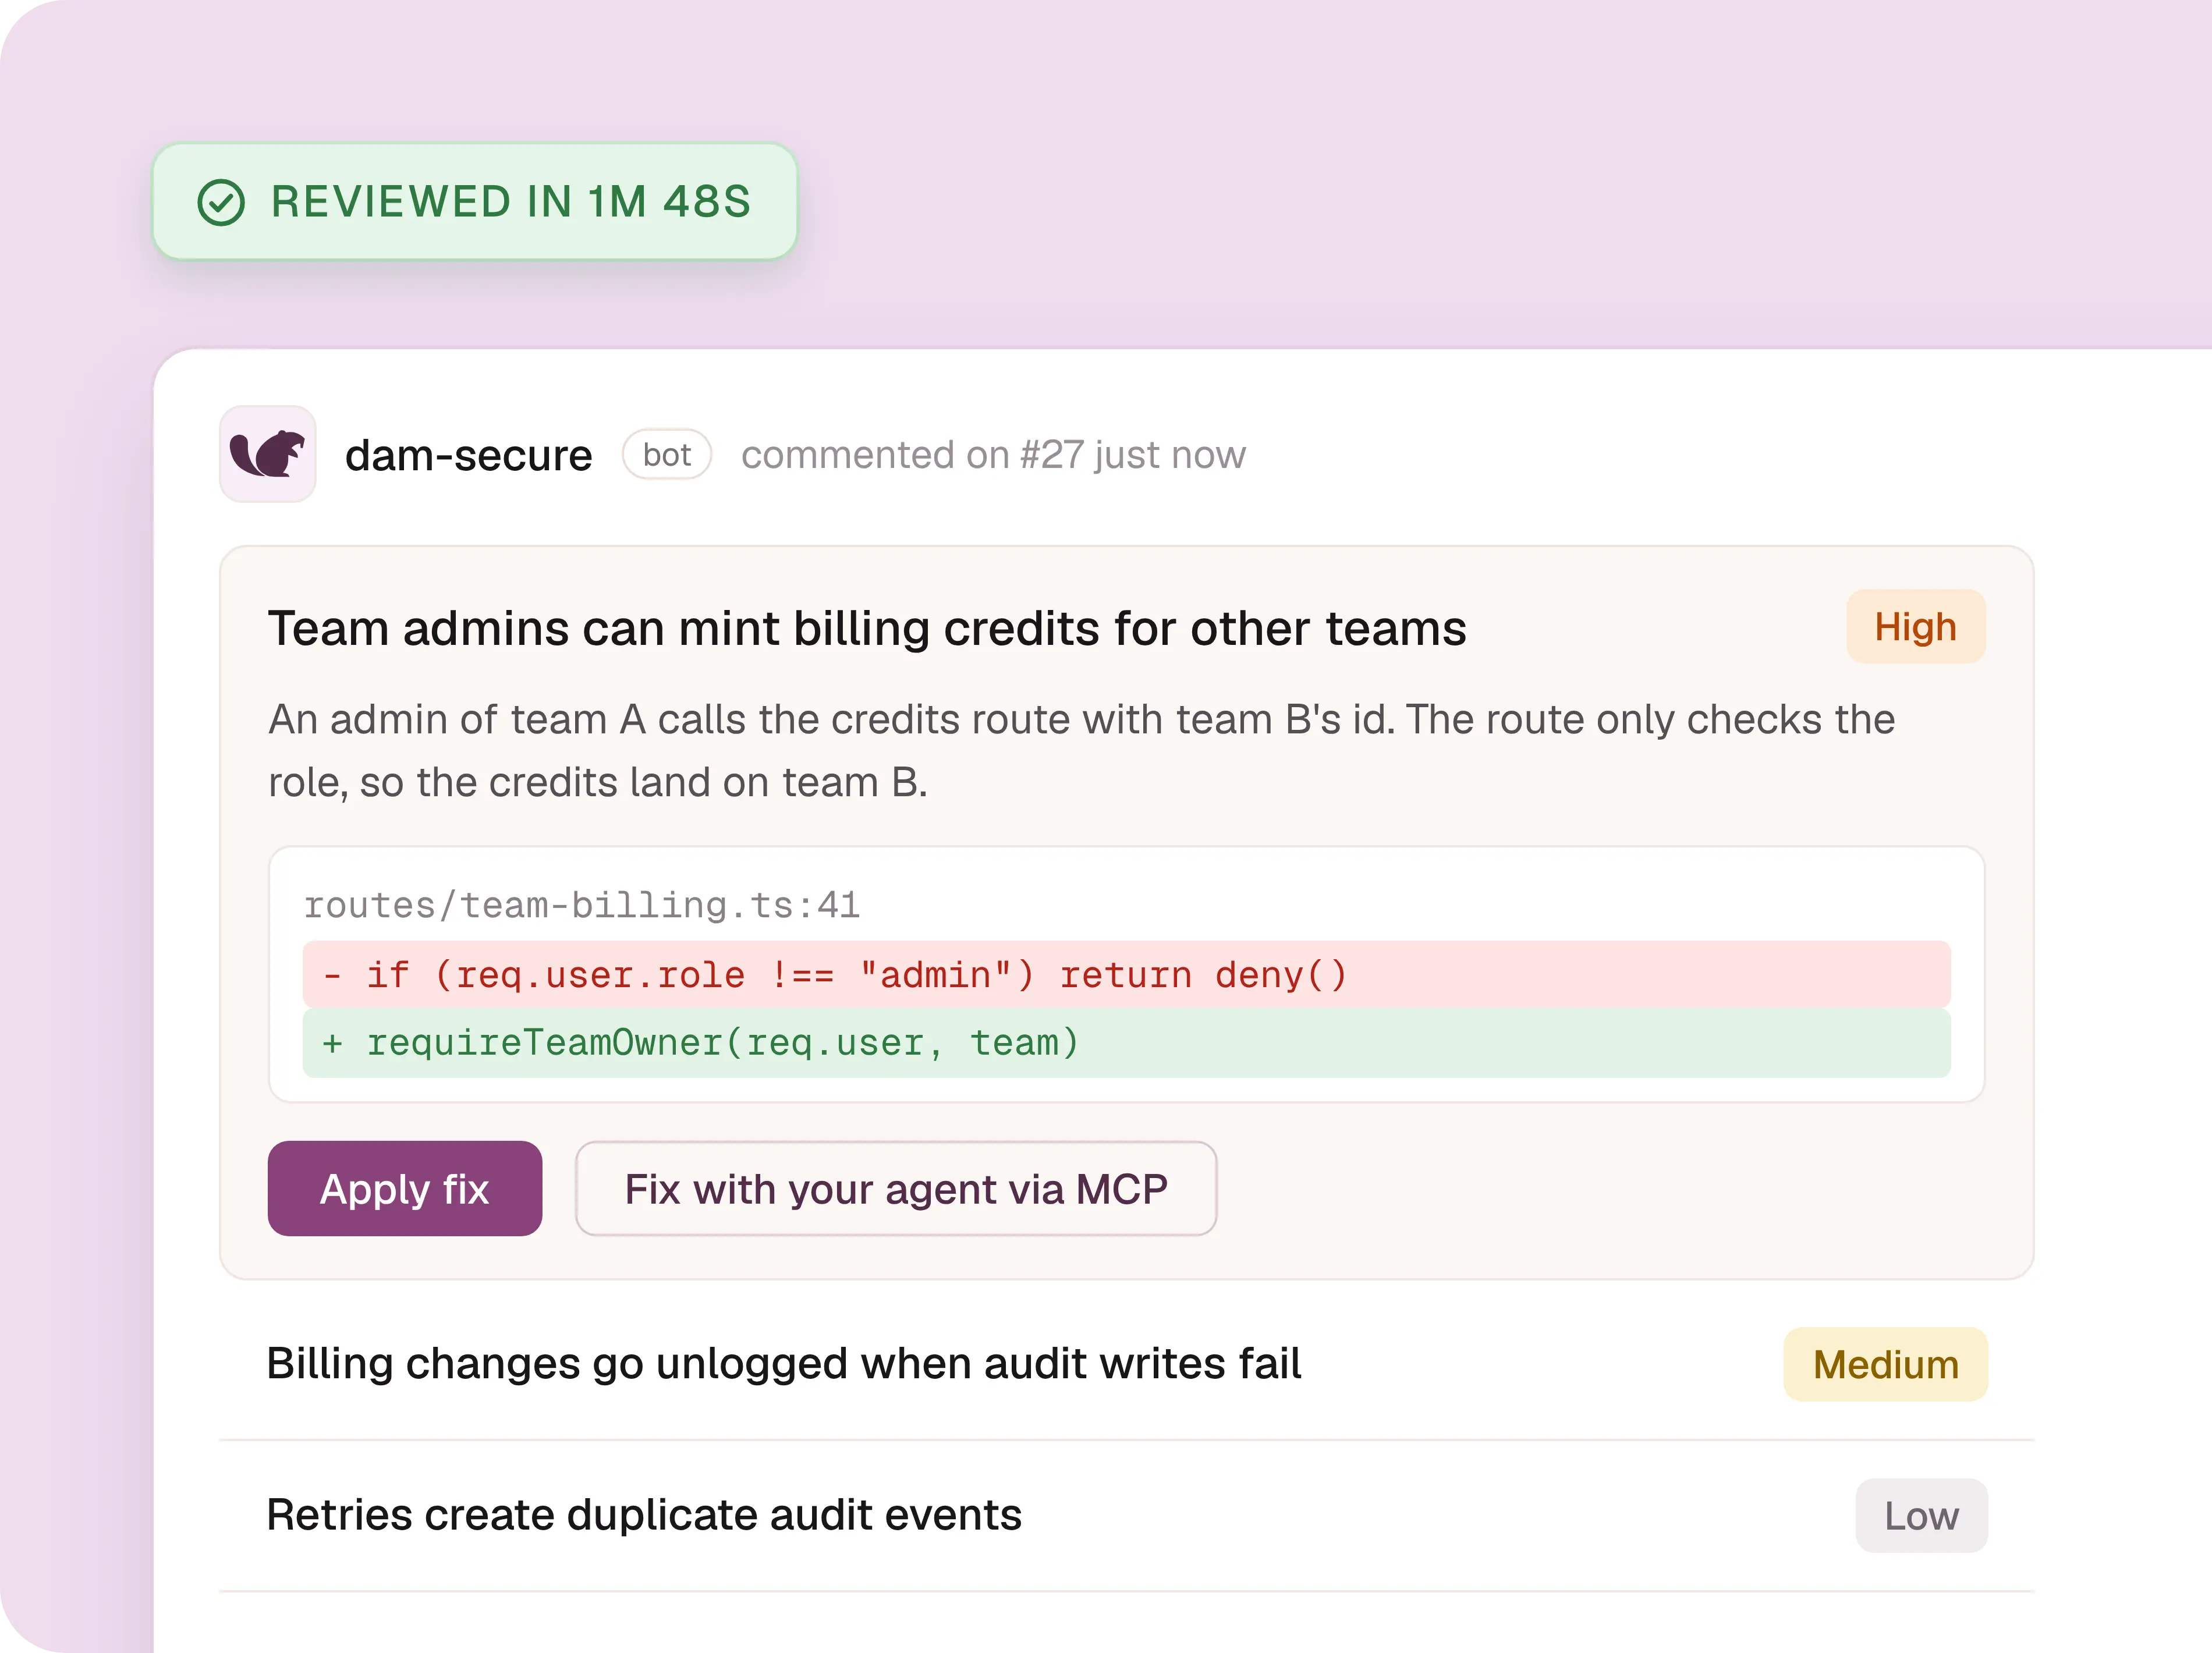
Dam Secure groups every known vulnerability by package and shows the version that fixes them. Your agents can pull the critical ones over MCP, so fixes start where the code gets written.
Turnkey support for 10 ecosystems.
Connect your repos and Dam Secure checks packages across npm, PyPI, Maven, Go and six more ecosystems, monorepos included. There’s no per-language setup and nothing to configure.
How it works
Connect your repos.
Install the GitHub App once for your org, or connect GitLab, Bitbucket or Azure DevOps. Dam Secure finds every package on its own.
Check every package.
Each package version is matched against known advisories across 10 ecosystems.
Triage the package findings.
Work through findings grouped by package, or pull them straight into your coding agent.
Works with the tools you already use



Your Security.
Enforced at AI Speed.
Attackers are already using Mythos-level models to find vulnerabilities. Join the teams putting frontier models on your side first.